HOW DO YOU ENFORCE CONTENT EXPIRATION ACROSS ENTERPRISE TEAMS?
September 30, 2026




A rep is three days from close. The buyer asks one more question about pricing, and the rep pulls up the deck they always use, the one that's worked a dozen times before. Except the numbers changed two quarters ago, and nobody told the deck. The buyer notices. Now the rep isn't selling anymore, they're explaining.
That's the failure mode content expiration is supposed to prevent, and it's rarely about one careless rep. It's what happens when nobody owns the decision to retire content, so nothing gets retired. Enterprise teams that actually enforce content expiration across enterprise teams do it the same way they enforce any other operational policy: by attaching ownership and a trigger to every asset, not by hoping people remember to check.
This is for RevOps, enablement, and content leads managing a library that multiple teams upload into, not a single content owner managing a tidy personal folder.
What "Content Expiration" Actually Means in an Enterprise Content Stack
A content expiration policy assigns an owner and a review date to every content asset, so the asset gets checked, refreshed, or retired on a schedule instead of sitting untouched indefinitely. It's a recurring checkpoint, not a one-time cleanup.
Search for the raw term and most of what comes back is about something else entirely: SharePoint links that stop working after 90 days, Teams recordings that auto-delete, Microsoft 365 groups that expire after 180 days of inactivity. That flavor of expiration lives inside a governance framework built around naming conventions, automated lifecycle policies, and periodic access reviews. It's a real discipline, and it's solving a different problem: storage cost and compliance risk, not whether the content itself still tells the truth.
Sales content expiration is a content-quality problem wearing a lifecycle costume. It's one stage of content lifecycle management: the same discipline that covers how an asset gets created and used, not a separate function bolted on afterward. A battlecard doesn't become a security risk when it goes stale. It becomes a liability the moment a rep trusts it in front of a buyer.
Where content actually lives when nobody's watching it
Every asset that lands in a proper hub moves through the same digital asset management life cycle: created, tagged, used, and reviewed again. Expiration is just the stage most teams never got around to building a process for.
A centralized content hub structure, the alternative to assets scattered across shared drives, inboxes, and internal wikis.
Why Manual Content Audits Don't Scale Past One Team
The standard advice for keeping a content library clean is a quarterly audit: someone sits down, reviews what's in the library, and flags what needs updating. That practice, paired with tagging every asset by type, audience, and sales stage, is exactly what most content-governance guidance recommends. It works fine when one person can realistically hold the whole library in their head.
It stops working the moment content lives in more than one place. Marketing uploads to the content hub. Product marketing keeps a separate folder for competitive intel. A regional sales team keeps its own deck on internal wiki software because the "official" version never quite fit their market. That's what internal content management looks like without a single owner: several small, well-intentioned systems, and nobody accountable for any of them going stale.
None of those teams did anything wrong. Each one solved a local problem the way it made sense to at the time. The cost shows up later, when a rep on a fourth team pulls whichever version their search turns up first, with no way to tell if it's the current one or a draft someone forgot to archive two reorgs ago.
Stale content isn't a minor annoyance either, it's a business risk: when collateral doesn't reflect the current product, buyers can feel misled after the sale closes, and that shows up as churn before it ever shows up as a lost deal. A quarterly calendar review catches maybe a fraction of that, and only for the content someone remembers to look at.
The Four Levers That Make Expiration Enforceable, Not Aspirational
Most teams already agree content should be reviewed. Very few have turned that agreement into something a system actually checks. Four things have to be in place before "we should really clean this up" becomes a policy instead of a New Year's resolution.
Ownership
Assigns one accountable person or role to every asset. Without it, nobody has the authority to retire content, so it just sits there indefinitely.
Review trigger
A date or usage threshold that fires automatically. Without it, review only happens when someone remembers, which is rarely.
Approval workflow
A lightweight refresh-or-retire decision, not a full campaign review. Without it, flagged content stalls in limbo instead of getting resolved.
Retirement rule
A default action if nobody responds: archive, restrict, or delete. Without it, untouched content stays fully visible and shareable by default.
Ownership is the lever teams skip most often, mostly because it feels like extra admin work up front. It's the opposite. Everything else on this list depends on someone being answerable for the call, whether that's the original author or a rotating content administrator role.
Turning four principles into an enforced policy
This is what separates a policy written in a doc from enterprise digital asset management that actually holds: ownership and permissions configured once in the platform, not re-explained to every new hire who joins a content team.
Ownership and access settings as a configurable part of the platform, not a spreadsheet someone maintains by hand.
Enforcing This Across Multiple Teams, Not Just One Library
Here's the part that's specifically an enterprise problem, not a small-team one: it's not hard to write a policy. It's hard to apply the same policy consistently once marketing, product marketing, and three regional sales teams all publish into a shared library.
Role-based permissions are what hold that together. They decide who can publish new content, who can approve a refresh, and who has the authority to override a retirement decision, all without a project manager chasing every team individually. A workable governance model connects policy, ownership, approvals, and retirement into one operating model, so every stakeholder works from current material and leadership can enforce compliance at scale rather than team by team.
Picture three regional sales teams and one central marketing org all publishing into the same hub. Without role-based permissions, "who's allowed to retire this asset" becomes a Slack thread every time someone disagrees. With them, the policy already answered the question before the disagreement started: the asset owner decides, and everyone else sees the outcome, not the debate.
Getting content hub operations right across five teams isn't about writing a stricter policy document, it's about making the permissions do the enforcing so the policy doesn't depend on everyone reading it.
Role and group settings that let one expiration policy hold across every team publishing into the same hub.
Tagging and Metadata: The Mechanism That Makes Expiration Automatic
Automating content expiration requires metadata attached at upload: an owner, a content type, a last-updated date, and a target audience or sales stage. Without those fields, there's nothing for an automated policy to evaluate, so every review defaults back to someone remembering to check manually.
Think of tagging as the difference between a filing cabinet and a search engine. A filing cabinet only works if you remember where you put something. A tagged, metadata-rich library can tell you on its own that thirty assets in the "competitive positioning" category haven't been touched since last quarter, without anyone going looking for them.
Metadata fields captured at the asset level, the input an automated expiration flag actually runs on.
Spotting Stale Content Before It Costs You a Deal
A calendar date is a reasonable trigger, but it's a blunt one. Some content ages in a month (anything with pricing in it). Some barely ages in a year (a foundational explainer on your category). Usage data catches what a fixed date misses: the assets nobody's opened in three months, regardless of how old they technically are.
When reps get caught without a ready answer mid-call, buyers notice, and it tends to cost the deal the trust it needed to close. Usage-based flags surface that risk before it plays out live in front of a buyer, instead of after.
There's a second, quieter signal worth watching alongside usage: content that gets opened constantly but never shared externally. That pattern usually means reps are checking it to confirm it's still accurate before they trust it, which is its own kind of warning sign, even if the asset technically hasn't expired yet.
Usage visibility that shows what's actually being opened and shared, versus what's quietly gone stale.
How Paperflite Enforces Content Expiration at the Enterprise Level
You don't need a separate expiration tool bolted onto your existing library. You need the four levers, ownership, triggers, approval, and retirement, built into the platform your teams already publish into.
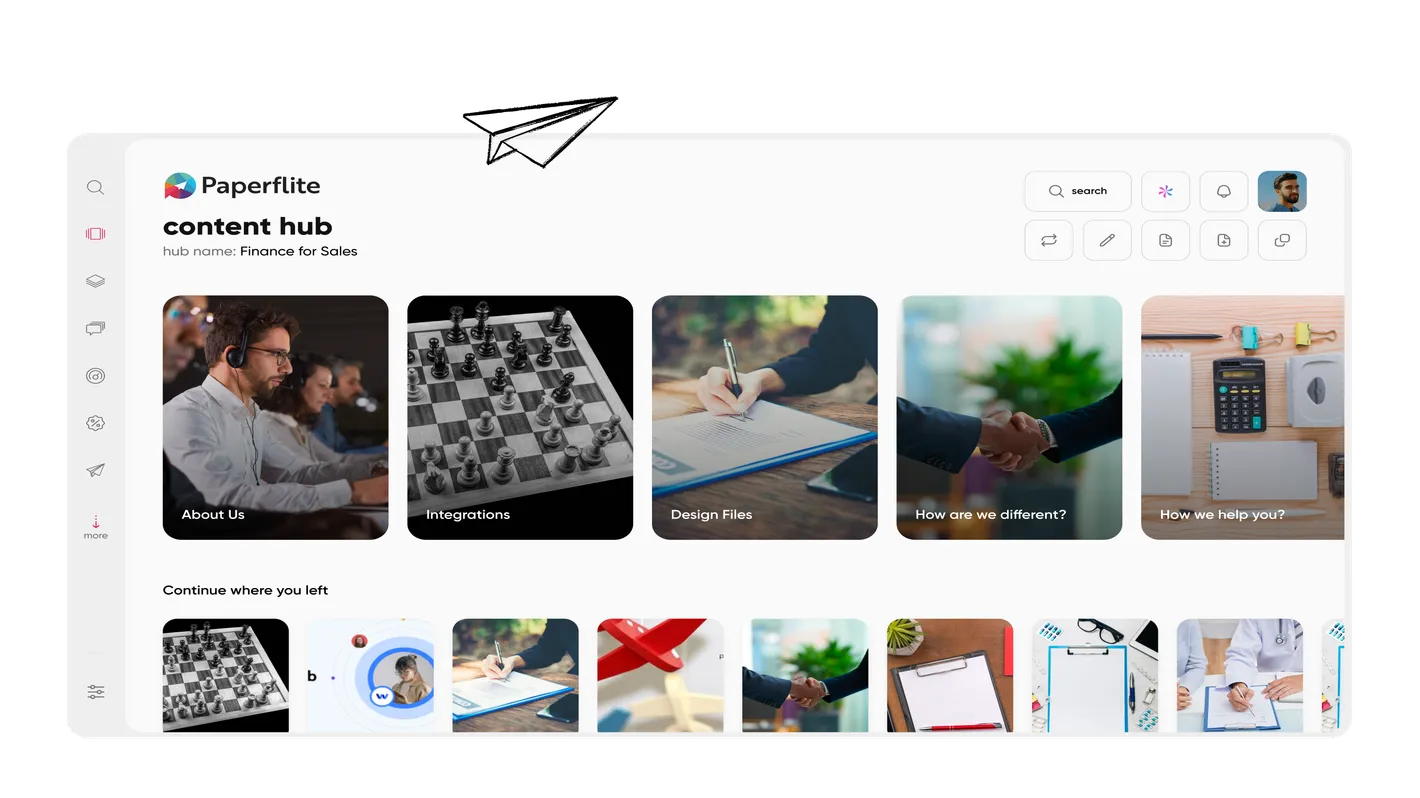
Paperflite's Content Hub handles this through role-based permissions, so ownership and publishing rights are set once and apply consistently across every team uploading into the hub. Every asset carries metadata at upload, content type, audience, sales stage, so flagging what's aging isn't a manual search, it's a filter. And RevOps reporting gives content leads a single view across the whole library instead of one team's slice of it, which is what actually makes enforcement possible at enterprise scale rather than aspirational. If you're weighing which content hub tools actually need to be in place before you can enforce a policy like this, ownership, tagging, and reporting are the three that matter most.
The fastest way to see it running against your own library is to book a demo.
A single content hub replacing scattered drives, wikis, and inboxes as the source of truth.
Executive-level visibility into content health across every team, not just one library.
Content expiration only works when it's built into the system, not into someone's memory. Ownership decides who's accountable. Triggers decide when a review happens. Permissions decide whether the policy actually holds once five teams are publishing into the same hub instead of one.
Get those three right, and content stops expiring quietly in the background and starts getting caught before a rep ever hands it to a buyer.
If you're still deciding whether a centralized hub makes sense for your team at all, what digital asset management is a good next read.
What is a content expiration policy?
A content expiration policy assigns an owner and a review date to every content asset, so it gets checked, refreshed, or retired on a schedule instead of sitting untouched indefinitely. The point isn't deletion, it's a recurring decision point.
How often should enterprise sales content be reviewed?
High-use assets like pricing decks and battlecards are worth reviewing quarterly. Lower-traffic assets can run on a longer cycle, ideally tied to a usage threshold rather than a fixed calendar date, since a piece nobody's opened in months is a stronger signal than its literal age.
Who owns content expiration in an organization?
Ownership usually sits with the asset's original author or a designated content administrator. Enablement or RevOps typically enforces the policy across teams through role-based permissions, so the rule holds even as more teams publish into the same library.
What happens when content expires in a content hub?
Depending on the policy, expired content is archived, access-restricted, or deleted by default. The owner can override that and renew the asset before the deadline hits, which is why ownership has to be assigned before a trigger date means anything.
How is content expiration different from content deletion?
Deletion is a one-time cleanup action taken after the fact. Expiration is a recurring checkpoint that forces a decision, refresh, retire, or renew, before the content has a chance to go stale and get shared with a buyer in the meantime.
What's the actual risk of not enforcing content expiration?
Reps end up sharing outdated pricing, positioning, or product claims with buyers. That erodes trust mid-deal, and if the mismatch surfaces after the sale closes, it tends to show up later as churn rather than as an obviously lost deal in the moment.
Frequently Asked Questions
PAPERFLITE'S CONTENT TECHNOLOGY IN ACTION
IT'S EASIER THAN FALLING OFF A LOG
(DON'T ASK US HOW WE KNOW THAT)